Offensive Security, Precision Engineered
Manual penetration testing of applications, networks and cloud, by a firm that has done nothing else since 2014. Findings reach your portal as they are approved, so your team is fixing on day three instead of reading a PDF on day thirty.
Our Services
Know what an attacker would actually reach
Scoped to what you run, tested by a consultant who owns the engagement from kickoff to retest. Every finding comes with the steps to reproduce it and a fix your engineers can act on.
Our Platform
The engagement lives in a portal, not an inbox
We built our own platform so that what you buy is visible while it happens: findings as they are approved, a conversation with the tester on each one, and retests from the same screen.
Findings the day they are approved
A consultant confirms it, a reviewer approves it, and it is in your portal with an email at the severity you choose. Nothing reaches you before that approval.
Ask the tester, on the finding
Every finding has its own thread. Your question goes to the people who tested it, and the answer comes back with a name and role on it, not a ticket number.
Retest from the same screen
Fix it, request a retest on the finding within the retest window, and the verdict appears once a reviewer approves it. Retesting is quoted in up front, not sold afterward.
What was actually tested
Hosts, open ports, services and breach credentials for your domains, mapped before testing starts, so you can check the scope you paid for was covered.
Into your own tools
Export to Jira with severity mapped to priority, download CSV, or pull findings through a read-only API into your own dashboards.
Year over year, same scope
Compare this year with last on the same scope, see what is still open and for how long, and start the renewal from what was tested last time.
What that means for you
Most firms run on scattered tools, Word templates and spreadsheets. We built one system covering the whole engagement, so you are never waiting on a PDF to find out what was found.
- Your own client portal with MFA, or your corporate SSO once we set it up
- Per-team access, so each team sees only the assessments it owns
- Your ticket references and owner notes on each finding, kept out of our report
- Report, executive summary and letter of attestation when you want them
- Reports delivered by expiring, revocable link, never as an email attachment
- Our AI report check sees a redacted copy, sent only to zero-retention model endpoints
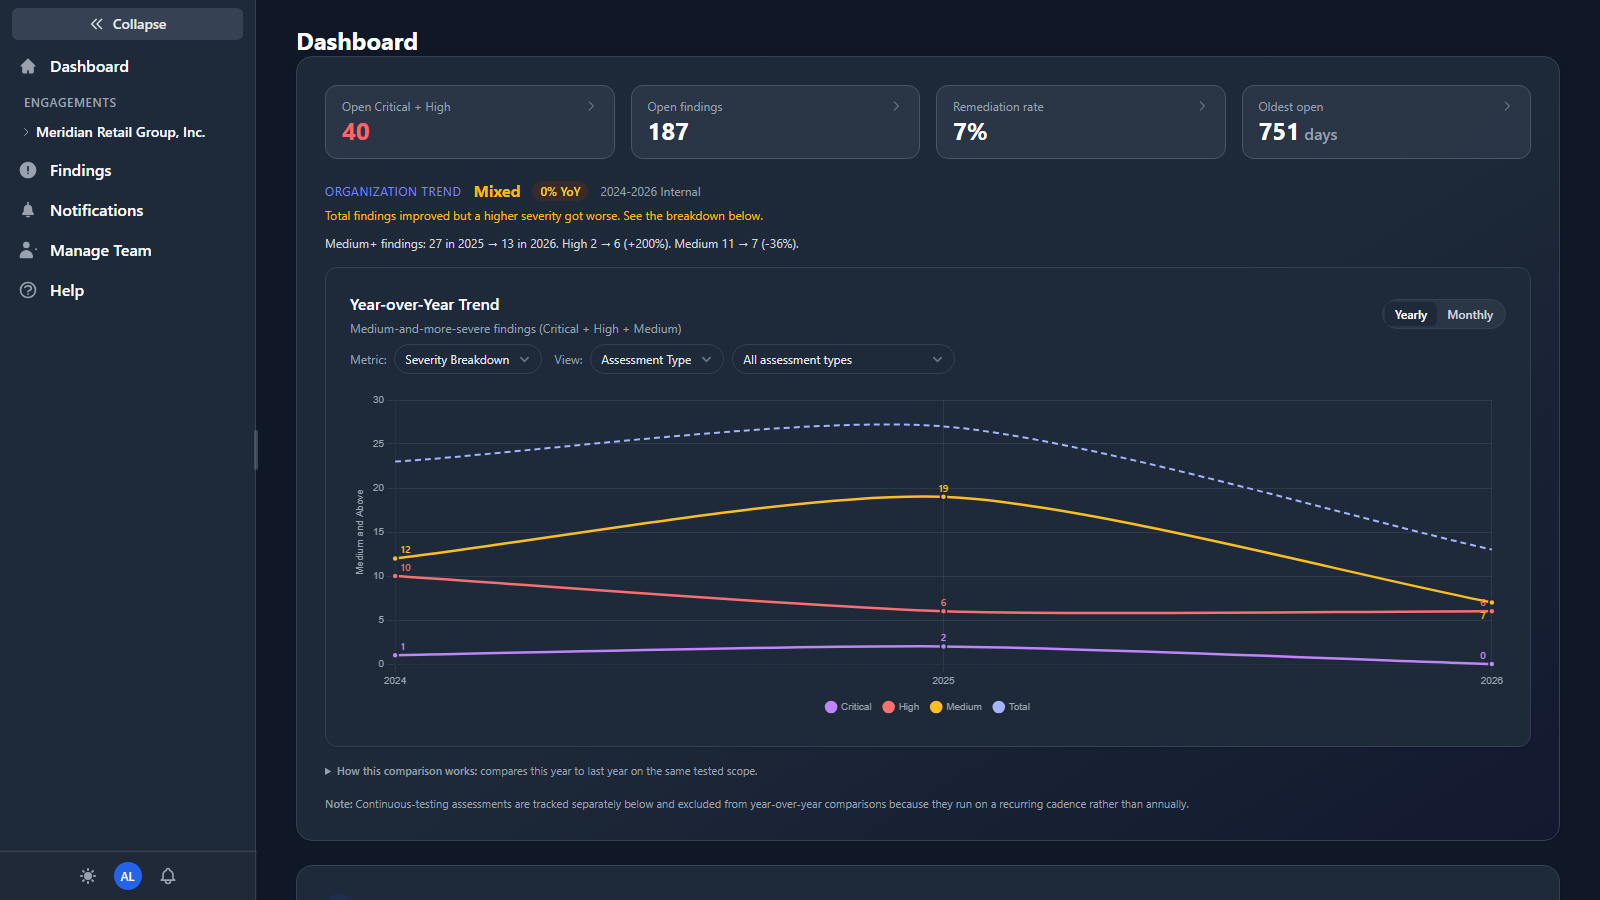
Your client portal: real-time findings, retest requests, and reports in one place
Client Testimonials
Clients mention the communication before the findings
Over 1,000 assessments delivered for 200+ organizations since 2014. Here's what our clients say about working with us.
“The quality of the work, findings, and reporting was phenomenal. The high level of communication and service really helped us stay on track and within our budget.”
“Professional and knowledgeable team; great communication; reporting is awesome; always responsive; and really strong technical skills. I trust that they have conducted thorough pentests and feel confident in the results.”
“TrustFoundry's communication top to bottom is hands down the best we've had from any partner we have used. This saved us a lot of frustration and time.”
“We wanted a vendor that had experience with Fortune 500 companies, and is quick to address our concerns. In TrustFoundry we found a partner that was organized, had deep expertise.”
“Trust Foundry is vital to our ongoing security and compliance efforts. Their ability to simulate real-world attack scenarios helps identify security weaknesses that other teams can miss.”
“Out of the gate our experience with TrustFoundry was very positive. They did their own scoping research, and not having to coordinate between sales and testers saved valuable time.”
The Foundry
Latest from Our Blog
Original security research, vulnerability disclosures, and technical deep-dives from our team.
Tell us what needs testing
Say what is in scope and what is driving the test: an audit, a customer questionnaire, a launch. We scope it with you and quote it with the hours and the methodology written down.
Prefer to talk now? Call (913) 871-3371